


WPFunnels: Critical RCE Vulnerability (CVE-2026-14345, CVSS 9.8)
Critical RCE vulnerability (CVSS 9.8) in the WordPress plugin WPFunnels: CVE-2026-14345 allows unauthenticated code execution. Update to version 3.12.8.
Read ArticleCurrent CVEs, vendor advisories, and specific recommendations for addressing critical security vulnerabilities.
Critical RCE vulnerability (CVSS 9.8) in the WordPress plugin WPFunnels: CVE-2026-14345 allows unauthenticated code execution. Update to version 3.12.8.
Read Article
Critical vulnerabilities in Plesk (CVE-2026-48614, CVE-2026-56843, CVSS 9.9) allow for privilege escalation and password disclosure. A patch is available for CVE-2026-56843.
Read Article
Analysis of critical vulnerabilities in Adobe ColdFusion (CVSS 10.0), including CVE-2026-48316 and CVE-2026-48282. CISA warns of active exploitation. Patches are available.
Read Article
Three critical Gitea vulnerabilities: CVE-2026-58426 (data access), CVE-2026-20896 (account takeover), CVE-2026-22874 (SSRF). Updating to version 1.26.4 is recommended.
Read Article
CVE-2026-9725 (CVSS 9.1) in the WordPress plugin Printcart allows unauthenticated deletion of arbitrary files. Update to version 2.5.3.
Read Article
CVE-2026-57677 (CVSS 9.8) in the Novalnet plugin for WooCommerce allows unauthenticated store takeover. Update to version 12.10.4.
Read Article
CVE-2026-37106 (DokuWiki): Not RCE, but a controversial account creation feature—only when self-registration is enabled (default: disabled). Assessment & Protection.
Read Article
INTERPOL reports a rise in cybercrime. At the same time, a Chrome zero-day vulnerability (CVE-2026-11645, CVSS 8.8) that is actively being exploited has come to light. Analysis and protective measures.
Read Article
Analysis of the critical remote code execution vulnerability CVE-2026-25470 (CVSS 10.0) in the WordPress plugin ACPT. Versions up to 2.0.47 are affected. Immediate action is required.
Read Article
A critical vulnerability, CVE-2026-49109 (CVSS 9.8), in the WordPress plugin cf7-salesforce allows PHP object injection. All versions <= 1.4.3 are affected.
Read Article
Analysis of the critical vulnerability CVE-2026-29116 (CVSS 8.7) in Dahua products. An unauthenticated attack could result in a denial of service. Recommended actions.
Read Article
Analysis of the critical vulnerability CVE-2025-12686 (CVSS 9.8) in Synology BeeStation, which allows unauthenticated remote code execution. Details and measures.
Read Article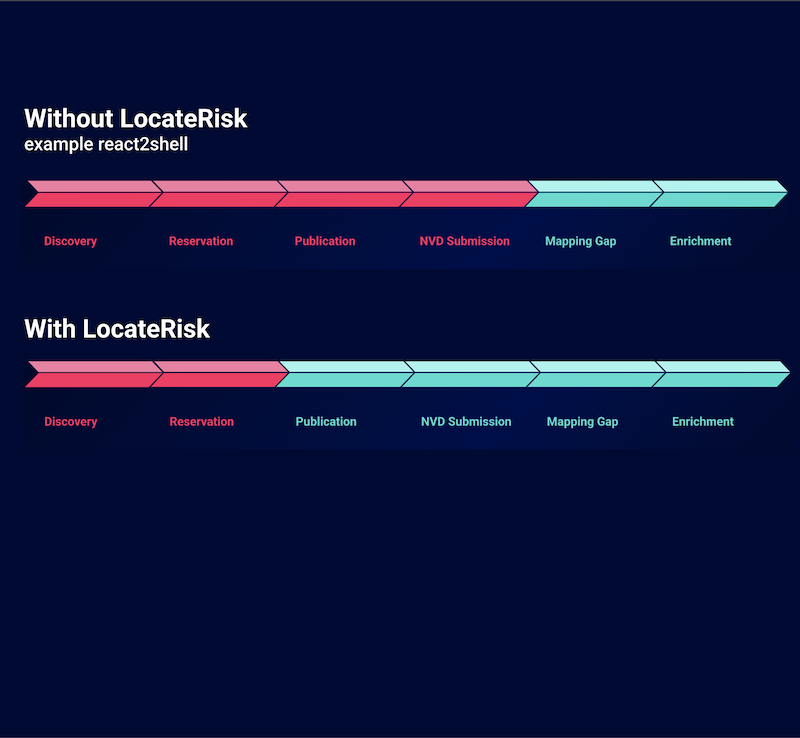
How to Use Preemptive Intelligence to Secure Critical Software Immediately After a Vulnerability Is Disclosed and Shorten the "Time to Action"
Read Article


 English
 Deutsch
 Français